
IoT Zero Trust Architecture: Security Guide
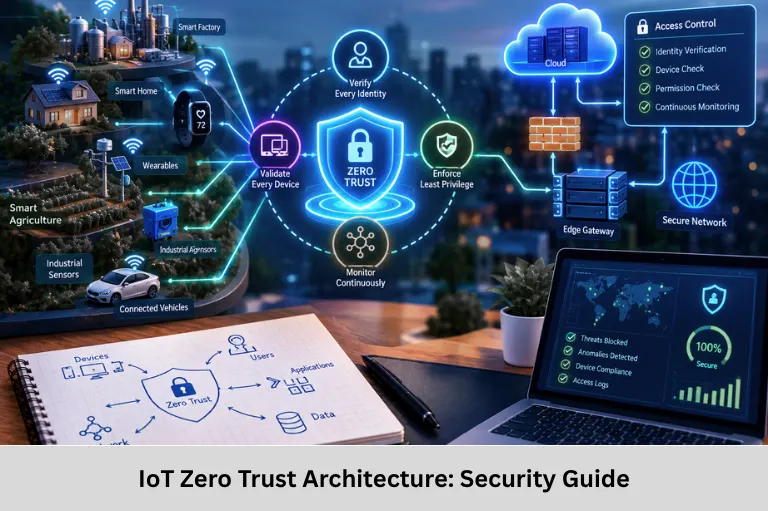
Learn Internet of Things (IoT) Zero Trust Architecture, device identity, micro-segmentation, mTLS, IAM, monitoring, ZTNA, SIEM, IIoT security and implementation. Embedded Tech Development Academy (ETDA).
- IoT Zero Trust Architecture: Security Guide
-
IoT Network Zero Trust Architecture
- Introduction to IoT Network Zero Trust Architecture
- Fundamentals of Zero Trust Security
- Why IoT Networks Require Zero Trust
- IoT Components of Zero Trust Architecture
- IoT Architecture Layers with Zero Trust
- Steps to Implement IoT Zero Trust
- Key Challenges in IoT Zero Trust
- IoT Security Technologies Supporting ZTA
- Zero Trust in Industrial IoT
- Frequently Asked Questions
- Conclusion
IoT Network Zero Trust Architecture
Introduction to IoT Network Zero Trust Architecture
The rapid expansion of the Internet of Things (IoT) has connected billions of sensors, gateways, controllers, industrial machines, medical devices, smart appliances, vehicles, and edge-computing systems to private and public networks. This connectivity improves automation and data collection, but it also increases the attack surface. Many Internet of Things (IoT) devices operate with limited CPU, memory, storage, and security capabilities, while some devices remain deployed for years with outdated firmware. Consequently, conventional perimeter-based security is insufficient for modern IoT environments.
Internet of Things (IoT) Zero Trust Architecture (ZTA) follows the principle “never trust, always verify.” Instead of assuming that a device is trustworthy because it is connected to an internal network, Zero Trust continuously evaluates identity, device posture, authorization, communication behavior, and resource access. Every connection must be authenticated and authorized according to defined security policies.
A technically implemented Internet of Things (IoT) Zero Trust model combines device identity management, mutual TLS, certificate-based authentication, secure boot, firmware integrity, micro-segmentation, least-privilege access, network monitoring, anomaly detection, policy enforcement, telemetry, SIEM/XDR integration, and automated incident response.
For engineers working with connected embedded systems, understanding Internet of Things (IoT) security architecture is increasingly important. Embedded Tech Development Academy (ETDA) provides practical technical training in Embedded C, Embedded Linux, Internet of Things (IoT), networking, cybersecurity fundamentals, and embedded development. Learners seeking a Top Embedded Training Institute in Bangalore can develop industry-oriented Internet of Things (IoT) security skills with assured placement support.
Fundamentals of Zero Trust Security
Never Trust, Always Verify
Zero Trust eliminates implicit trust. A user, device, application, or service must prove its identity and authorization before accessing a protected resource.
Core Zero Trust Principles
The major principles include:
- Continuous authentication and authorization
- Least-privilege access
- Strong device identity
- Explicit policy enforcement
- Continuous monitoring
- Assume breach
- Micro-segmentation
- Real-time risk assessment
Least-Privilege Access
An Internet of Things (IoT) device should receive only the permissions required for its specific function. For example, a temperature sensor may be allowed to publish temperature measurements to one MQTT topic but should not be allowed to access configuration servers or unrelated devices.
Why IoT Networks Require Zero Trust
Large-Scale Device Deployment
Internet of Things (IoT) environments may contain thousands or millions of devices distributed across factories, buildings, vehicles, homes, and remote locations.
IoT Security Weaknesses
Common weaknesses include:
- Weak authentication
- Default credentials
- Limited processing resources
- Outdated firmware
- Insecure communication protocols
- Poor credential management
- Long device lifecycles
- Physical exposure
- Remote deployment
Limitations of Perimeter Security
Traditional security assumes that devices inside a protected network are relatively trustworthy. Internet of Things (IoT) environments invalidate this assumption because a compromised sensor, gateway, or controller can become an entry point for lateral movement.
IoT Components of Zero Trust Architecture
Device Identity and Access Management
Every Internet of Things (IoT) device should have a unique, verifiable identity.
Identity Technologies
Device identity can be established using:
- X.509 certificates
- Hardware-backed keys
- TPMs
- Secure elements
- Cryptographic credentials
- Device attestation
Identity Lifecycle
Identity management should cover device provisioning, certificate issuance, authentication, credential rotation, revocation, renewal, and secure device decommissioning.
Micro-Segmentation
Micro-segmentation divides an Internet of Things (IoT) environment into smaller security zones.
Network Enforcement
VLANs, firewalls, SDN, access-control lists, and gateway policies can restrict communication between devices.
Limiting Lateral Movement
If one sensor is compromised, segmentation can prevent the attacker from directly communicating with PLCs, databases, engineering workstations, or other Internet of Things (IoT) devices.
Continuous Monitoring and Analytics
Zero Trust requires continuous visibility into device behavior.
Behavioral Telemetry
Security monitoring can analyze:
- Source and destination addresses
- Ports and protocols
- Connection frequency
- Data volumes
- Authentication events
- Firmware state
- Command patterns
Anomaly Detection
A sensor that normally communicates with one gateway but suddenly starts transmitting large amounts of data to an unknown external IP address can trigger an anomaly alert.
Policy Enforcement Point
A Policy Enforcement Point (PEP) controls access between a device and a protected resource.
Access Decision
The enforcement point evaluates the result of authorization policies before permitting communication.
Distributed Enforcement
PEPs may exist at Internet of Things (IoT) gateways, network firewalls, proxies, cloud services, or device-level security components.
Security Gateways and Proxies
Internet of Things (IoT) gateways can provide a centralized enforcement layer between constrained devices and external networks.
Gateway Functions
A secure Internet of Things (IoT) gateway can perform:
- Device authentication
- TLS termination where appropriate
- Protocol inspection
- Access control
- Logging
- Network segmentation
- Certificate validation
Edge Security
Gateway-based enforcement is particularly useful when individual Internet of Things (IoT) devices have limited resources for implementing sophisticated security controls.
IoT Architecture Layers with Zero Trust
Device Layer
The device layer contains sensors, actuators, PLCs, microcontrollers, cameras, and embedded controllers.
Device Security
Security controls include secure boot, hardware-backed keys, signed firmware, device identity, and firmware integrity verification.
Trusted Execution
Where supported, secure elements, TPMs, or trusted execution mechanisms can protect cryptographic material and security-sensitive operations.
Edge and Gateway Layer
The edge layer aggregates Internet of Things (IoT) traffic and applies security policies close to the devices.
Gateway Enforcement
The gateway can authenticate devices, inspect traffic, enforce segmentation, and forward authorized data.
Reduced Attack Surface
Restricting direct device-to-device communication reduces opportunities for lateral attacks.
Network Layer
The network layer provides connectivity while enforcing segmentation and traffic policies.
Secure Communication
Protocols such as TLS and mutual TLS can provide encryption and endpoint authentication.
Traffic Control
Firewalls, VLANs, SDN policies, and access-control rules can restrict unauthorized communication paths.
Cloud and Application Layer
Cloud platforms receive telemetry and provide dashboards, analytics, storage, and control services.
Application Authorization
Cloud APIs should authenticate clients and authorize requests using device identity, application identity, roles, attributes, and security policies.
Continuous Verification
Cloud access should remain subject to authorization policies rather than being automatically trusted because a request originates from an internal network.
Steps to Implement IoT Zero Trust
Step 1 – Discover and Identify Devices
Create an accurate inventory of all Internet of Things (IoT) assets.
Device Inventory
Record device identity, firmware version, network address, ownership, function, location, and security status.
Unique Identity
Provision each device with a unique cryptographic identity rather than using shared credentials.
Step 2 – Establish Secure Communication
Use authenticated and encrypted communication channels.
Mutual TLS
mTLS authenticates both communicating endpoints using certificates and protects data against interception and unauthorized access.
Credential Protection
Avoid hard-coded passwords and unprotected private keys. Hardware-backed key storage should be used where available.
Step 3 – Implement Fine-Grained Authorization
Define exactly what each device can access.
Attribute-Based Access Control
ABAC can evaluate attributes such as device identity, device type, location, firmware status, resource sensitivity, and requested operation.
Least Privilege
A device should only receive permissions necessary for its operational function.
Step 4 – Implement Micro-Segmentation
Group devices according to role, sensitivity, and function.
Segmentation Technologies
Use VLANs, SDN, firewall policies, gateway ACLs, and security groups.
Isolation Strategy
Compromised devices should be automatically restricted from sensitive systems.
Step 5 – Monitor Telemetry Continuously
Collect security and operational telemetry.
Real-Time Detection
Monitoring systems can identify abnormal traffic, authentication failures, unusual commands, and unexpected firmware changes.
Automated Response
Security policies can automatically quarantine devices that exhibit suspicious behavior.
Step 6 – Automate Incident Response
Automation reduces response time during security incidents.
Quarantine Operations
A compromised device can be isolated from production networks.
Recovery
Security automation can initiate certificate revocation, firmware remediation, device re-provisioning, or controlled recovery procedures.
Key Challenges in IoT Zero Trust
Resource Constraints
Many Internet of Things (IoT) devices have limited RAM, flash, processing power, and battery capacity.
Cryptographic Overhead
TLS, certificate validation, logging, and continuous monitoring can consume computational and memory resources.
Engineering Trade-Off
Security controls must be designed according to device capabilities without eliminating essential protections.
Device Diversity
Internet of Things (IoT) environments contain devices using different operating systems, processors, communication protocols, and firmware architectures.
Legacy Devices
Older devices may not support modern authentication or encryption mechanisms.
Migration Strategy
Legacy devices may require secure gateways, network isolation, compensating controls, or phased replacement.
Scalability
Managing certificates, policies, telemetry, and identities across thousands of devices is complex.
Automated Provisioning
Automated identity provisioning and certificate lifecycle management reduce operational overhead.
Centralized Visibility
SIEM and XDR platforms can aggregate security events from distributed Internet of Things (IoT) environments.
IoT Security Technologies Supporting ZTA
Device Identity Technologies
X.509 certificates, TPMs, secure elements, device attestation, and hardware-backed cryptographic keys establish device trust.
Secure Boot and Firmware Integrity
Secure boot verifies that only authenticated firmware is executed during system startup.
Zero Trust Network Access
ZTNA applies identity-aware access controls instead of relying on network location as the primary trust mechanism.
IoT Security Gateways
Gateways can provide authentication, authorization, protocol inspection, logging, and segmentation.
SIEM and XDR Integration
Security Information and Event Management and Extended Detection and Response platforms can correlate telemetry from devices, networks, applications, and cloud systems.
Zero Trust in Industrial IoT
IIoT Factory Example
Consider an industrial environment containing PLCs, sensors, HMIs, industrial gateways, and supervisory systems.
Device Authentication
Each PLC and critical sensor can possess a unique certificate-based identity.
Communication Policy
A sensor should communicate only with its authorized gateway or controller. Direct communication with unrelated systems should be blocked.
Automated Threat Detection
If a sensor suddenly communicates with an unknown IP address, the monitoring system can generate an alert.
Policy-Based Isolation
The gateway or network enforcement system can automatically isolate the device.
Industrial Continuity
Security controls must be carefully designed so that isolation does not unnecessarily interrupt safety-critical or production processes
Frequently Asked Questions
What is Zero Trust Architecture in IoT?
IoT Zero Trust Architecture is a security model that continuously verifies devices, users, applications, and communication requests instead of automatically trusting devices based on their network location.
Why is Zero Trust important for IoT?
IoT environments contain large numbers of distributed and heterogeneous devices, many with limited security capabilities. Zero Trust reduces unauthorized access and limits lateral movement after compromise.
How does mTLS improve IoT security?
Mutual TLS authenticates both communication endpoints using cryptographic certificates while encrypting network traffic. This helps prevent unauthorized devices from impersonating trusted endpoints.
What is micro-segmentation in IoT?
Micro-segmentation divides an IoT network into smaller security zones and restricts communication between them. This limits lateral movement when a device is compromised.
Can Zero Trust be used in Industrial IoT?
Yes. Zero Trust principles can be applied to PLCs, sensors, HMIs, gateways, and industrial applications through device identity, segmentation, least privilege, continuous monitoring, and policy-based access control.
Conclusion
Internet of Things (IoT) Network Zero Trust Architecture is a strategic security architecture for protecting distributed, heterogeneous, and highly connected Internet of Things (IoT) environments. Instead of assuming that a device is trustworthy because it exists inside a private network, Zero Trust requires explicit authentication, authorization, continuous monitoring, and policy enforcement for every important access request.
A complete Internet of Things (IoT) Zero Trust implementation combines device identity, X.509 certificates, mutual TLS, secure boot, firmware integrity, least-privilege authorization, micro-segmentation, security gateways, telemetry, anomaly detection, SIEM/XDR integration, ZTNA, and automated incident response. These mechanisms work together to reduce unauthorized access and limit the impact of compromised devices.
For resource-constrained embedded systems, Zero Trust must be implemented with careful consideration of CPU utilization, memory consumption, cryptographic processing, battery life, network bandwidth, and firmware capabilities. Security architecture should therefore be matched to device capabilities rather than applying identical controls to every Internet of Things (IoT) endpoint.
Embedded Tech Development Academy (ETDA) provides practical learning in embedded systems, Internet of Things (IoT) architecture, networking, Embedded C, Embedded Linux, microcontrollers, and security-oriented development. Learners looking for a Top Embedded Training Institute in Bangalore can build practical technical knowledge of connected devices and Internet of Things (IoT) security with assured placement support.
A strong Top Embedded Training Institute in Bangalore approach should teach Internet of Things (IoT) security beyond theoretical authentication concepts. Engineers need practical understanding of certificates, TLS/mTLS, device provisioning, secure boot, firmware updates, network segmentation, gateways, MQTT security, access-control policies, telemetry, and incident response. Embedded Tech Development Academy (ETDA) can help learners connect these concepts with practical embedded systems and Internet of Things (IoT) development while providing assured placement support.
The architecture should also evolve as the deployment grows. Organizations can begin by identifying critical devices, establishing unique identities, securing communication channels, implementing least-privilege policies, and segmenting sensitive systems. Continuous monitoring and automated response can then be added progressively.
As industrial automation, smart infrastructure, connected vehicles, healthcare devices, and edge computing expand, Zero Trust becomes increasingly relevant to embedded systems security. Embedded Tech Development Academy (ETDA) supports industry-oriented technical learning in these areas, helping learners understand how a Top Embedded Training Institute in Bangalore environment can combine embedded development, Internet of Things (IoT) networking, cybersecurity concepts, and practical projects with assured placement support.
Ultimately, Zero Trust is not a single security product. It is a continuously enforced security strategy based on identity verification, least privilege, segmentation, encryption, device integrity, continuous monitoring, and automated response. Applying these principles correctly enables organizations to build more resilient Internet of Things (IoT) networks while reducing the consequences of device compromise and unauthorized lateral movement.
Author: ETDA Trainers
Experience: 10+ Years of Industry Experience in Embedded Systems, IoT, and Embedded C Programming